

Welcome to The Cybersecurity Pulse (TCP)! I’m Darwin Salazar, Head of Growth at Monad and former detection engineer at Datadog. Each week, I bring you the latest security innovation and industry news. Subscribe to receive weekly updates! 📧
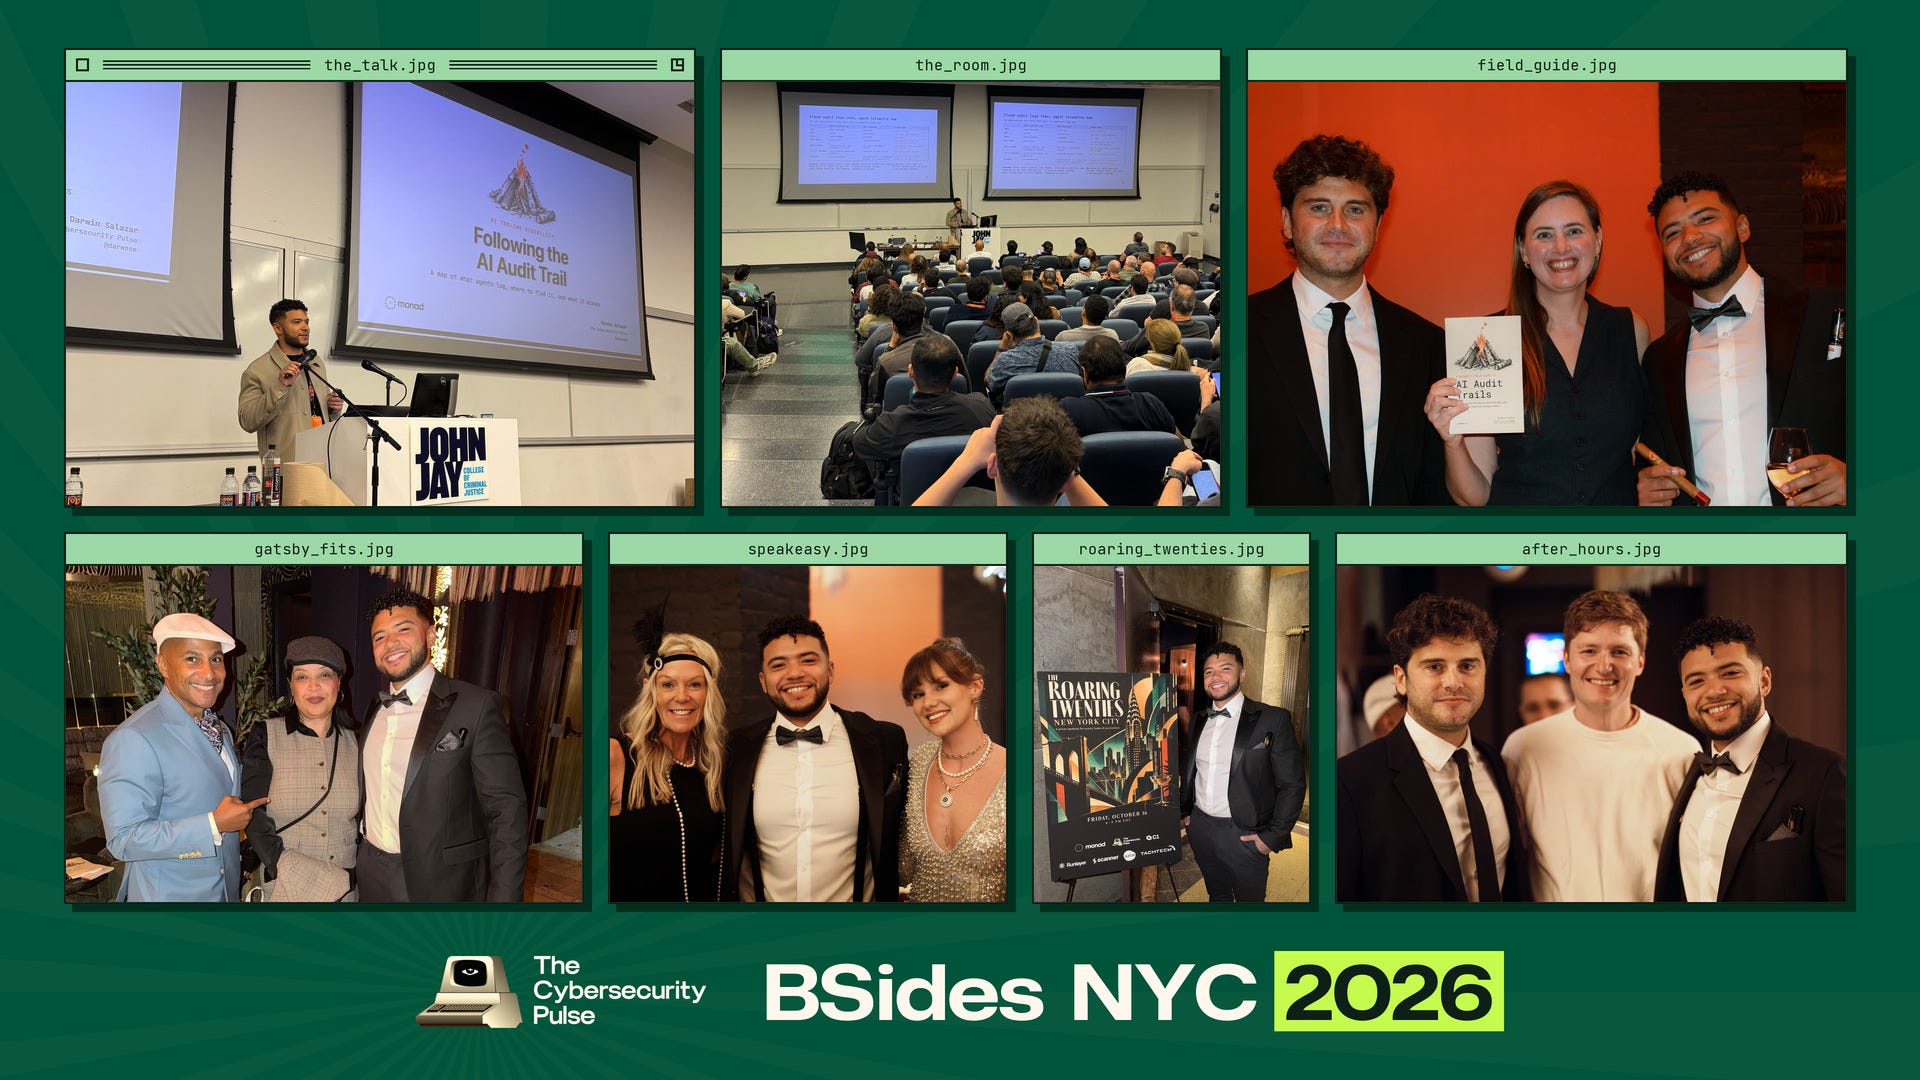
Howdy 👋 Checking in quickly here as I’m still riding the high from this past weekend in NYC for BSides! I remember attending BSides Boston while still a junior in college. It’s a place where folks across all career levels come together to learn, give back, and just be. That community feel is a big part of what keeps me coming back.
BSides NYC was extra special because I got to present some of the AI audit log research we’ve been working on at Monad AND we received copies of our refreshed book, which lands on Amazon tomorrow! Keep an eye out for TCP #150 for more on that!
We also hosted a Gatsby-themed Roaring Twenties pre-game on Friday night. More on that below.
On the personal front, last week was packed. Mom’s birthday, meeting our newborn niece, travel, announcing Andrew Richards as TCP’s new contributing writer, and finally getting to hang out with him. All of this on top of event planning, book + presentation shenanigans. One of the busier weeks of the year for me.
Following the AI Audit Trail
AI logs in 2026 feel a lot like cloud logs did in 2019.
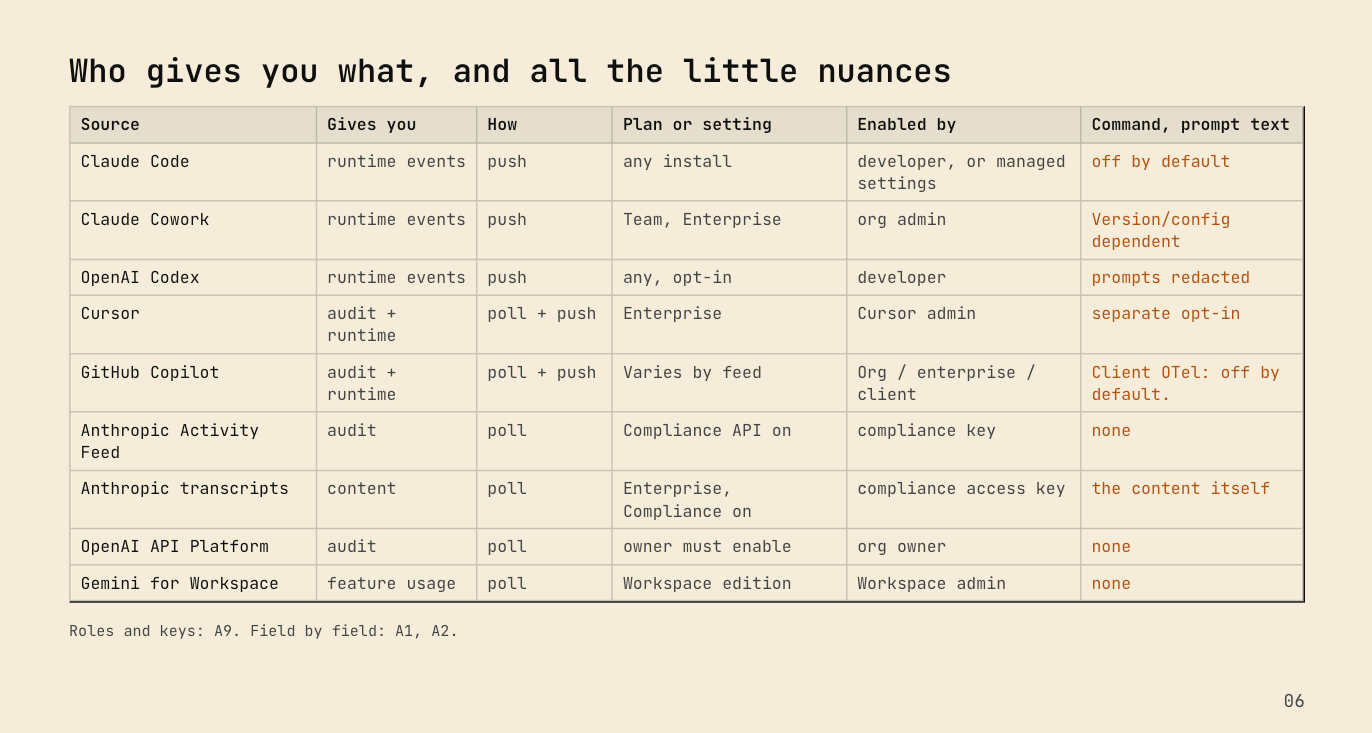
The tools keep changing, and so do their logs. New fields, products being merged (i.e., Claude Cowork x Claude unified). Lots of quirks across providers, data types, and the tools behave + record activity differently so understanding the nuances are key to defending your org.
At Monad, we’ve been working through what each source records, how to collect it, and which fields help with detection, response, and investigations. That research also feeds into the we’re launching tomorrow.
Talk slides are up on Github. We covered:
What agents can access. Agents can read local files, run commands, and call cloud or SaaS APIs using the permissions and credentials available to them.
What each log records. Platform audit logs show account, API key, and policy changes. Runtime events show tool calls and approval decisions. Transcripts show prompts and responses. Endpoint logs help confirm which commands ran and which files changed.
How to collect the logs. Required plans, permissions, and settings vary by tool. Client telemetry needs to be enabled before the activity happens. You can’t turn it on afterward and recover the missing events.
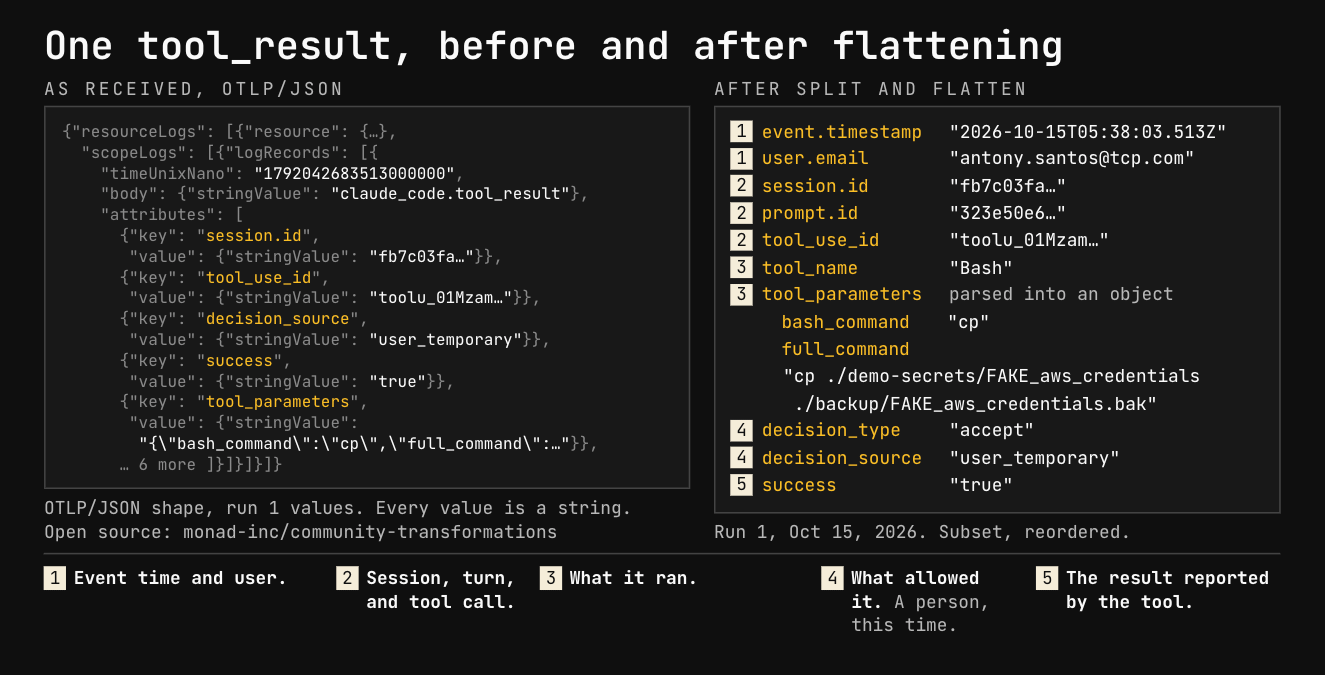
How to connect related events in Claude Code.
session.idgroups events from one session.prompt.idgroups events from one prompt.tool_use_idconnects a tool call’s approval decision with its result.Why blocked commands matter. Claude Code records rejected calls in
tool_decision, without a correspondingtool_result. If you only search tool results, you miss those rejected attempts.
For the demo, I asked Claude Code to copy a fake credentials file. I approved one attempt, rejected another, and let auto mode handle a third. We compared the logs from each run.
The morning after I ran those scenarios, Claude Code added two new fields to its OpenTelemetry tool_decision events: classifier_verdict and permission_mode.
So I got to update the slides and prove my own point at the same time.. AI audit logging moves fast.
I also poked a little fun at Gemini for Workspace’s audit logging. Those activity logs show where Gemini was invoked from (i.e., Drive, Gmail, Sheets) and who did it, but don’t include the prompts and responses. Afterward, I got a message from a TPM who’d been in the crowd. Always fun finding out the vendor was in the room lol.
Big shout-out to Kenneth Kaye, Valerie Worman, Matt Jane, and Curtis Redgate for their contributions to the research + book.
Full transparency, I still get quite a bit of jitters and often ask myself “why did I sign up for this?” before speaking to a large crowd. I’m always happy with the result + conversations after and it does help me build that muscle, but I think 2-3 talks per year is a good sweet spot for me lol.
Friday night at Bar Bas
Before the conference, we got everyone together at Bar Bas for our Roaring Twenties pre-game. The room was swanky, people had fun with the theme, and I got to finally meet folks I’d only known online.
I loved getting to hang out, catch up, and dance a little after all the planning that went into it. Thank you to everyone who came through!
Huge thank-you to Runlayer, C1, Monad, Scanner, TachTech, and Surf AI for helping make it happen, and to Cyversity NYC for joining us as our community partner.
Afterward, we headed to dinner to celebrate the birthday of my dear friend Christian, Monad’s CEO.
Books + the rest of BSides
We gave away copies of the book throughout the weekend, and getting to physically hand it to people was pretty special after spending so much time working on it.
I spent most of the rest of Saturday hanging with friends. Didn’t catch as many talks as I wanted to, unfortunately, but I’m grateful for the time I got with everyone.
Huge love to the BSides NYC organizers, volunteers, and speakers for putting this together. And to the folks who started BSides, including Jack Daniel. It’s pretty cool to think about going from a college student attending BSides to sharing our own research with this community years later.
And to anyone working on BSides Austin: please bring it back soon. ASAP, ideally lol. We need more of this at home.